Dutch Arrest in ShinyHunters Probe Puts Cyber Risk Back in Market Focus
The case underscores how data theft and extortion risks continue to shadow digital finance, telecom infrastructure and technology stocks.
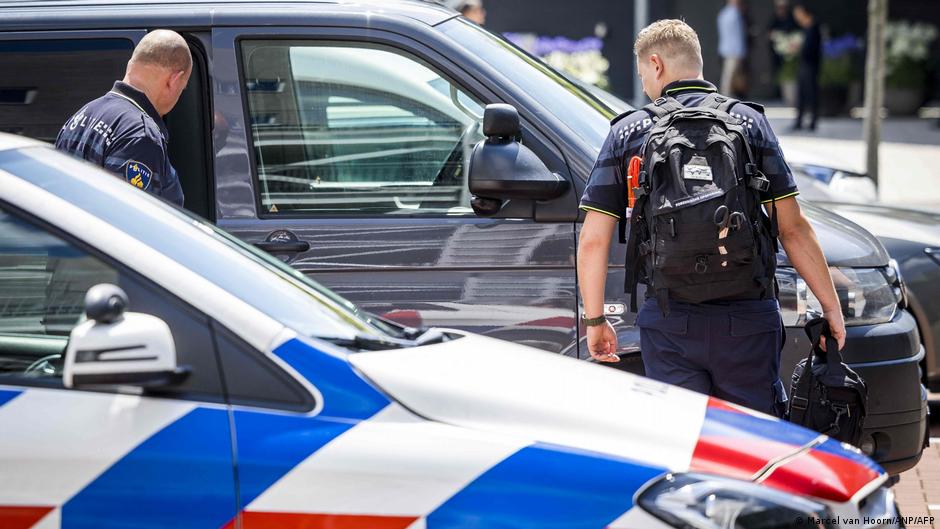
Dutch police have detained a 24-year-old Amsterdam resident as part of an investigation into ShinyHunters, the hacking group that last week claimed to have breached a database linked to FBI agents and stolen information on bureau personnel. The arrest places another high-profile cyber case at the intersection of law enforcement, corporate security and the digital economy.
Police in the Netherlands announced on Monday, September 28, that a 24-year-old man from Amsterdam had been detained in connection with the investigation into ShinyHunters. The exact date of the arrest was not given in the police statement on X, with authorities saying only that it took place in September. The suspect was due to appear before a court in Rotterdam on Tuesday, September 29.
The police did not disclose the suspect’s name. However, Benjamin Korper, a representative of Amsterdam cybersecurity company Neo Security, told Reuters that the detained man was Pepijn van der Stap, who leads the company’s offensive cybersecurity unit. According to Korper, his employee was arrested on September 15 “during a large-scale police operation involving flashbang grenades.” Forensic officers visited Neo Security’s office the same day.
ShinyHunters has denied that van der Stap has any connection to the group. The denial comes as the group faces renewed attention after claiming access to sensitive FBI-related data and after being linked to several other major breaches affecting telecom, gaming and education platforms.
Cybersecurity Credentials Under Scrutiny
The case is likely to resonate across the financial technology and digital banking sectors because it highlights one of the industry’s most difficult risk questions: how to assess people, vendors and security teams entrusted with offensive cyber capabilities. Fintech firms, crypto platforms and banks increasingly rely on external experts to probe vulnerabilities, run penetration tests and strengthen defenses against account takeover, ransomware, payment fraud and data theft.
Van der Stap had previously been convicted in 2023 and sentenced to four years in prison, one of them suspended, after a court found him guilty of a series of data thefts and extortion. Law enforcement authorities estimated that he earned between 1.5 million and 2.7 million euros from those crimes.
Investigators said those offenses were committed while van der Stap worked at Hadrian, an Amsterdam-based cybersecurity startup, and volunteered at DIVD, a nonprofit research organization that searched for computer vulnerabilities. During the trial, he admitted guilt and expressed remorse.
Van der Stap was released early in December 2025. Shortly before the new detention, he told Brian Krebs, the author of the KrebsonSecurity blog, that he was a hacker who had chosen a path of reform, wanted to change his life for the better and sought to benefit society. Korper described his employment at Neo Security as a “second chance” for his employee.
ShinyHunters said van der Stap “has nothing to do” with the group.
For digital finance executives, the episode illustrates the tension between hiring scarce security talent and managing reputational, regulatory and operational exposure. In payments and online banking, a single compromised system can expose identity data, enable social engineering, or create downstream fraud risks across merchants, processors and customer accounts.
Data Breaches as Digital Economy Risk
On September 22, ShinyHunters posted a message on the dark web claiming it had breached an FBI database and stolen data on many former and current bureau employees. The group claimed the data included information on psychiatric and medical examinations of agents. It also claimed to have accessed data belonging to FBI Director Kash Patel. Reuters was able to partially verify the authenticity of the published data.
FBI representatives said they were “aware of claims of unauthorized activity” affecting the FBIjobs.gov applicant website and were investigating.
Although the FBI case is not a financial-sector breach, its implications are broader. Digital banking, fintech lending, crypto exchanges and payment companies operate in an environment where stolen identity records, employee data and medical or background information can be used for targeted phishing, credential theft and extortion. Attackers often combine fragments from unrelated leaks to build convincing fraud attempts against institutions and their customers.
ShinyHunters has also been connected to several other major data leaks. In February 2026, after databases belonging to Odido, the largest mobile operator in the Netherlands, were hacked, the group obtained access to data on more than 6.2 million residents of the country. Mobile operators are central to the payments and authentication stack, with phone numbers frequently used in account recovery, customer verification and transaction alerts.
Other recent attacks attributed to ShinyHunters include the alleged theft of millions of corporate records from video game developer Rockstar Games, known for the Grand Theft Auto series, and a May attack on the Canvas educational platform that caused large-scale disruptions in U.S. schools.
For technology stocks and listed digital infrastructure providers, the pattern reinforces why cyber incidents remain a material market risk. Breaches can trigger regulatory scrutiny, customer churn, litigation, incident-response costs and pressure on valuations. Telecom operators, software platforms, cybersecurity vendors and fintech firms all face investor questions over resilience, disclosure and the quality of their internal controls.
The Dutch case is still at the investigation stage, and authorities have not publicly named the detained suspect. But the allegations surrounding ShinyHunters, the claimed FBI-related breach and the group’s links to earlier data incidents show how cybercrime continues to move across borders and sectors. In the digital economy, trust is infrastructure, and attacks on identity data, employee records and core platforms can quickly become financial risk.