Romania Uncovers Russian-Linked Sabotage Network Targeting Arms Plant
The alleged operation highlights growing physical and cyber risks to Europe’s interconnected defense, satellite and digital infrastructure.
Romania’s domestic intelligence service said it had uncovered a Russia-coordinated sabotage network that previously attempted to set fire to an industrial facility, widening European concerns about threats to defense production and the technology infrastructure supporting regional security.
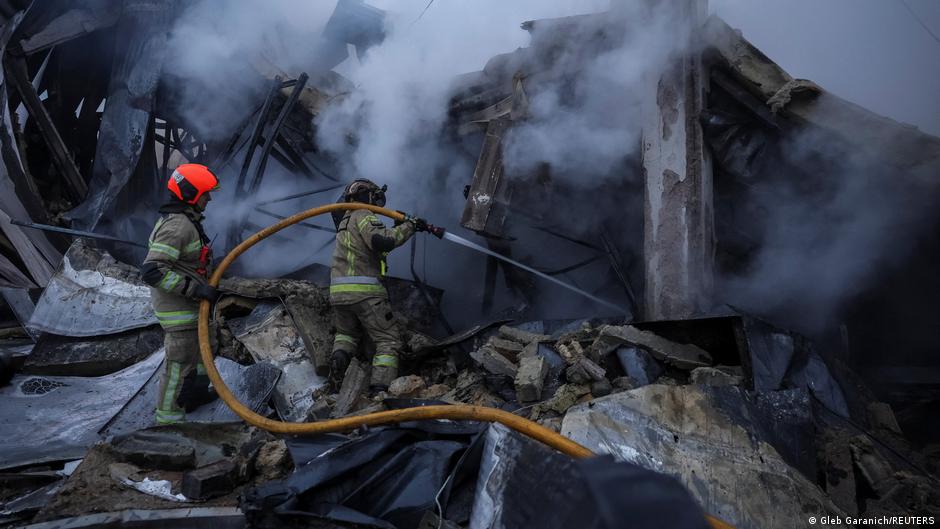
The Romanian Intelligence Service, known as SRI, said on Monday, October 26, that the network was “directly coordinated by the intelligence services of the Russian Federation.” According to the agency, the group attempted on September 14 to set fire to the Carfil weapons manufacturing plant in Brașov, a city in central Romania.
The case has immediate implications for Europe’s defense-industrial economy, but it also points to broader operational risks for technology companies, satellite networks and the digital systems used by manufacturers, banks and logistics providers. Physical disruption at a strategic factory can spread through digitally connected supply chains, affecting procurement, cross-border payments and investor assessments of regional security risk.
“Coordinators from the Russian Federation identified an extensive list of targets in the region for the group: state-owned and private arms manufacturers, as well as other sites of military and industrial interest,” Romanian intelligence said.
Reuters was unable to reach the Russian Embassy in Bucharest for immediate comment. Moscow has repeatedly denied similar allegations.
Cross-border network raises compliance and security concerns
The suspects include two Belarusian citizens and one Ukrainian citizen. Two were detained in Germany while preparing similar acts of sabotage, while the third is wanted in Poland, Romanian television channel Știri reported. Bucharest is seeking their extradition to Romania.
The investigation adds to a pattern of alleged cross-border operations that can create additional compliance demands for European financial institutions and digital payment providers. Banks and fintech platforms already screen transactions for sanctions violations, fraud and money laundering; cases involving recruitment payments and operatives moving between jurisdictions may increase scrutiny of small transfers, online identities and payment trails linked to suspected hostile activity.
A year earlier, Poland and Romania detained eight people suspected of involvement in a Russian plan to send parcels containing explosives to Ukraine. The latest case therefore reaches beyond the security of one Romanian factory and reinforces concerns about transport networks, parcel systems and the financial channels that may support clandestine operations.
Romania is a member of both the European Union and NATO and shares a land border of more than 600 kilometers with Ukraine. Romanian President Nicușor Dan previously said the country was a target of hybrid warfare conducted by Russia to destabilize states supporting Ukraine’s defense against Russian military aggression.
Romanian Foreign Minister Dan Nicolaescu described the fire in Brașov as “part of a broader sabotage campaign across Europe” directed against defense production, according to AFP.
Social media recruitment meets critical-infrastructure risk
SRI said people used in such operations are typically recruited through social networks. Prospective recruits are initially offered money for a “seemingly harmless task,” such as monitoring or photographing particular sites.
“Subsequently, the tasks become increasingly serious and may include acts of vandalism, arson or even murder,” the intelligence service said.
The reported recruitment method places online platforms, digital identity systems and payment services near the center of the security challenge. Social media can provide access to potential recruits, while electronic communications and payments may generate evidence for investigators. For digital banks and fintech companies operating across the EU, the allegations underscore the overlap between cybersecurity, transaction monitoring and the protection of critical infrastructure.
The Wall Street Journal reported on October 20, citing three European officials familiar with US intelligence findings, that Russian President Vladimir Putin had personally ordered an escalation of sabotage operations against NATO countries. According to the newspaper, an unsuccessful drone attack at Germany’s Leipzig airport on August 4 was among the first operations in the campaign.
After the incident, the Russian side warned the German government through an unofficial communications channel that Leipzig would not be the final target, according to people familiar with the conversation. The intensification of covert operations coincided with a lack of significant advances by the Russian military in Ukraine and increasingly frequent Ukrainian strikes on sites deep inside Russian territory.
Satellite and drone infrastructure emerge as targets
A series of further incidents followed Leipzig. Drone-manufacturing facilities in Estonia and Poland were set on fire in August, while Slovak authorities said they had prevented an arson attack against similar production. Poland, Lithuania and Bulgaria also reported sabotage targeting ground stations used by the Starlink satellite system.
Those incidents broaden the potential exposure from traditional arms makers to technology suppliers and communications infrastructure. Drone production and satellite connectivity sit at the intersection of defense, advanced manufacturing and the digital economy. Any sustained threat to those assets could influence cybersecurity spending, insurance costs and sentiment toward publicly traded European defense and technology companies, although the source reports did not quantify any financial impact.
Western officials said the sabotage activity was organized by the Special Tasks Department of the Main Directorate of the General Staff of the Russian Armed Forces, a unit created after the start of Russia’s military invasion of Ukraine. The department is headed by Colonel General Andrei Averyanov. Western intelligence services also determined that Colonel Denis Smolyaninov, one of the unit’s leaders, was involved in the Leipzig operation, the Journal reported.
For Europe’s financial and technology sectors, the Romanian case illustrates how hybrid threats can connect physical attacks, online recruitment, cross-border money flows and disruption of strategically important networks. The investigation and extradition efforts will now test cooperation among European intelligence agencies, law-enforcement bodies and the institutions responsible for monitoring the continent’s increasingly digital economy.